Training

Container Security

A hands-on in-company workshop for software developers and DevOps engineers

Why

Benefits

Containers ship fast. Security vulnerabilities ship with them if you're not careful.

Stop shipping vulnerabilities you don't know about

Container images are full of software: base OS layers, dependencies, and your application code. Each layer can contain known CVEs that automated pipelines package and deploy. This training teaches your team to find and address those vulnerabilities before they reach production.

Container security for DevOps work

Developers and DevOps engineers work with Dockerfiles, image scans, cluster settings, and pipeline checks they already recognize.

Hands-on from day one, no setup required

Participants get their own prepared cloud instance for the entire training. They can start the exercises immediately instead of spending the first hour fixing local setup issues.

Threat analysis for containerized workloads

The training includes hands-on threat analysis specific to container environments. Your team will work through the attack vectors that matter for containerized workloads: image tampering, namespace escapes, insecure defaults, and resource abuse.

Secure defaults your team can verify

Hardening a Dockerfile or a Kubernetes cluster gets easier once you know what to look for. This training covers the settings and checks that reduce risk, then has your team apply them in the lab environment.

Build a security mindset across your DevOps team

Developers and engineers make better security decisions when they know what to look for in images, manifests, and runtime settings. This training builds that awareness with the people who build and run the containers.

Price

In-Company Practitioner Training

Full-day workshop for software developers and DevOps engineers

Essentials

€5700 +VAT

Container security workshop covering threat analysis, hardening techniques, and production-style tooling.

  • Onsite / remote options
  • Cloud training instances included (no setup needed)
  • Container fundamentals refresher
  • Threat analysis and attack vectors
  • Image hardening and Dockerfile security
  • Cluster and network security
  • Vulnerability detection tooling
  • Secure container practices
Request a quote

Complete

€6900 +VAT

Workshop plus follow-up calls to apply the training to your Dockerfiles and pipelines.

  • Essentials training, plus:
  • 2 container security review follow-up calls (1 hour each)
  • 1 review of your team's Dockerfiles and pipeline configuration (2 hours)
Request a quote

Customized

Let's talk

Training adapted to your stack, cluster setup, or compliance requirements.

Schedule a call

Agenda

Topic outline

Introduction to Container Security

  • Goals of the Container Security Training
  • Container security in modern application development
  • Target audience and training focus
  • Introduction to DevOps principles
  • Integrating security into DevOps practices
  • Security considerations in the DevOps lifecycle

Container Fundamentals

  • Understanding containerization technology
  • Key concepts of containers
  • Network isolation in containers and clusters
  • User namespaces
  • Docker vs. Podman
  • Image analysis with Dive

Threat Analysis

  • Hands-on analysis of threats when using containers
  • Identifying common vulnerabilities and attack vectors
  • Analyzing container security risks
  • Exploring resource-limiting techniques

Security Measures

  • Implementing security measures for clusters, images, and containers
  • Techniques for securing container sources and Dockerfiles
  • Detection of known vulnerabilities
  • Addressing insecure image sources

Details

Trainers

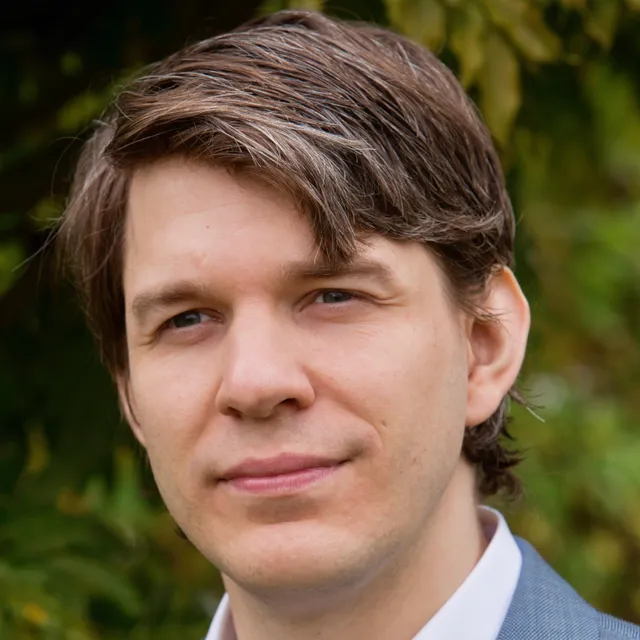
Timo Pagel

Timo Pagel

DevSecOps Architect

Timo Pagel is a DevSecOps architect with 25+ years of experience who integrates security into development lifecycles, leads OWASP projects, and provides security training and consulting.

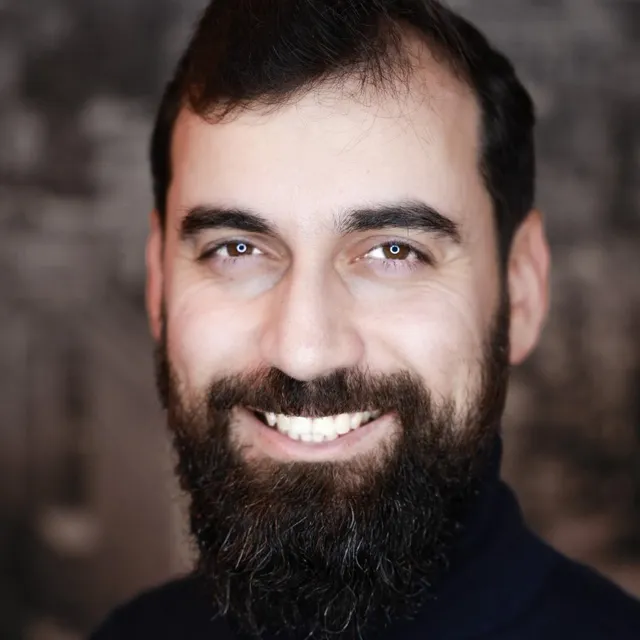
Nariman Aga-Tagiyev

Nariman Aga-Tagiyev

Product Security Architect

Nariman Aga-Tagiyev is an Application Security Architect with more than 20 years of experience in software development. He has worked as a full-stack web application developer, backend developer, DevOps engineer, and cloud developer. Since 2016, he has focused fully on application security work.

Details

FAQ

1. Who is this training for?
Software developers and DevOps engineers who work with containers day to day and want to understand how to build and run them securely. Participants should be comfortable with the basics of software development and IT systems. Prior hands-on experience with containers is helpful. If your team has not worked with Docker before, we recommend pre-reading to bring everyone up to speed.
2. What prior knowledge is needed?
Participants should have basic familiarity with container technologies such as Docker. If some team members do not, we recommend working through the Play with Docker beginner training beforehand. Basic Linux knowledge is also assumed; the Ryan's Tutorials Linux guide covers what participants need.
3. Do participants need to set up anything?
No. Each participant gets their own prepared cloud training instance. Participants only need an SSH client, such as PuTTY, to connect.
4. What tooling does the training cover?
The training uses tools participants are likely to meet in production: Dive for image analysis, plus standard tooling for vulnerability scanning and Dockerfile linting. The techniques transfer to whatever stack your team runs.
5. Can the training be delivered remotely?
Yes. The cloud-based training environment works equally well for remote delivery. Teams connect to their instances from wherever they are, and the trainer runs the session through a video call with screen sharing and breakout sessions as needed.
6. What facilities are needed for onsite delivery?
  1. A projector and power outlet for the trainer
  2. Each participant needs a laptop with an SSH client installed (PuTTY or equivalent)
  3. Reliable internet access, because participants connect to cloud instances throughout the training

Watch online

Container Security Scanning: Timo Pagel

Make it happen

Request a quote

We’ll prepare a quote for your purchasing team within 24 hours. No spam afterward.

Prefer email? Write to us and we'll get back within one business day.

Email training@securehabits.nl