Vulnerability Notification
Notify ENISA without undue delay when an actively exploited vulnerability is identified.
Free
Validate your product security strategy and confirm your readiness for the Cyber Resilience Act.
What
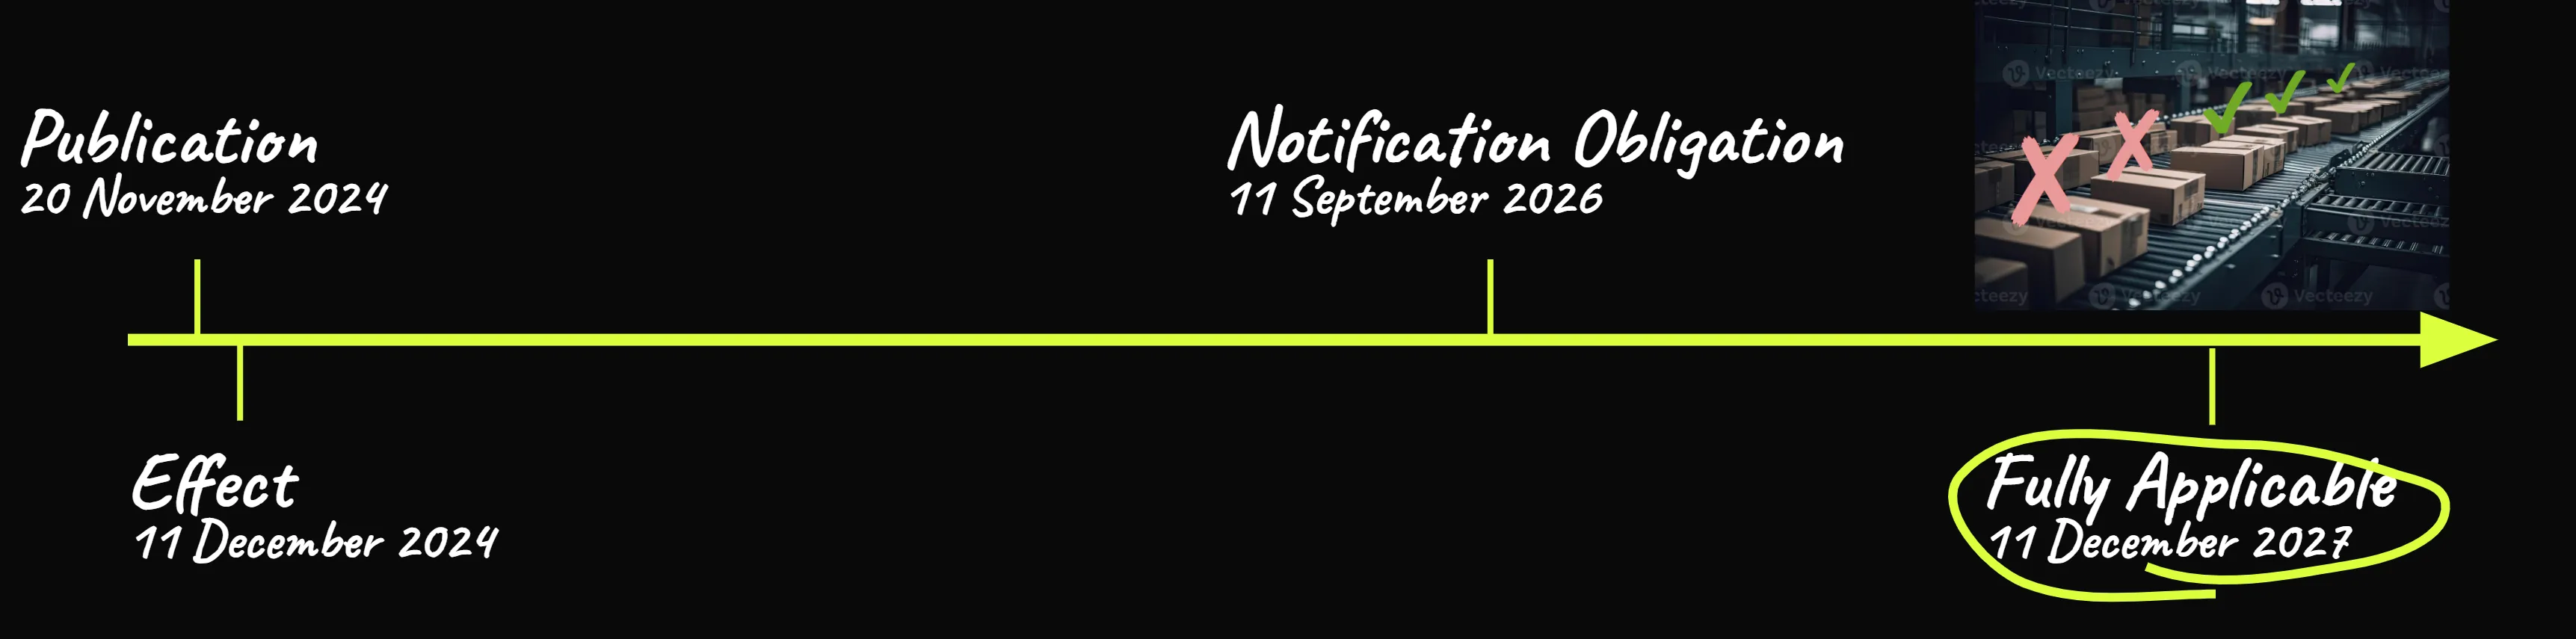
Notification Obligation
11 September 2026
Notify ENISA without undue delay when an actively exploited vulnerability is identified.
Report severe security incidents that significantly impact product security.
Submit an initial incident notification within 24 hours of awareness.
Provide a detailed follow-up report including mitigation measures.
Inform affected users and customers when action or mitigation is required.
Maintain documented records of all incidents, vulnerabilities, and notifications.
Full conformity
11 December 2027
Formally declare that the product complies with all applicable CRA requirements before placing it on the market.
Maintain technical documentation that shows compliance throughout the product lifecycle.
Build security into the product architecture from the earliest design stages.
Ship products with secure default configurations that require minimal user action.
Implement ongoing processes to identify, assess, remediate, and disclose vulnerabilities.
Pick a time
Our CRA specialists offer a free, one-hour health check of your EU CRA compliance strategy. There is no purchase requirement.
There is no catch. SecureHabits team members also volunteer in nonprofit initiatives such as OWASP and ISO, and we want more teams to understand what the CRA expects before the deadlines arrive.
We do not expect a work assignment after the health check. If the report uncovers work where we can help, we can talk about it. Either way, you leave with a clearer plan.
This health check is for manufacturers of products with digital elements or on-premises software who plan to sell their products on the European market.
If you already work with internal teams or external consultants on CRA compliance, we can review your current strategy and point out gaps before they become delivery problems.
The EU Cyber Resilience Act focuses on the security of the products you place on the European market. Its primary concern is the risk to your end users.
The ideal participants for this call are product owners, development managers, and members of application security teams.
After the call, our team will send a report on the current state of your secure software development lifecycle. We’ll highlight gaps that may lead to unacceptable risk.
You’ll also receive a list of missing controls required for baseline CRA compliance, along with an effort estimate for the work needed to reach baseline compliance.
After you receive the report and CRA readiness recommendations, we follow up only if you ask us to.
If you want help with the next steps, we can discuss the work at your pace.