
SSDLC Maturity Assessment & Roadmap
- Assess your current practices
- Prepare a roadmap to meet EU CRA and other regulations
- Turn assessment findings into practices teams can run themselves
- Create policies and documentation for legal evidence
Security by design
From SSDLC maturity to EU CRA compliance, we help your teams build secure-by-design products.

We strengthen application security with assessments, guidance, and training that fit into your delivery process.

Understand your current maturity and risks

Train, coach, and turn agreed controls into daily work.

Hand over security routines your teams can run without us

We bring threat modeling into design work, and secure-coding guidance into implementation, review, and release preparation.

Developers, architects, product owners, and security champions practice writing security requirements, reviewing risky flows, and assigning follow-up work.

Your teams keep using threat modeling, secure-coding guidance, and roadmap reviews after the engagement ends.
All-in-one AppSec platform for software supply chain security
Application security maturity management platform
Developer-centric application security training platform
Katilyst equips security champions to run engagement programs and reinforce secure behavior.
Securing guides teams through scoping, testing, report review, and remediation.
Offensive security, threat detection, incident response, and security operations for regulated and high-risk environments.
Application Security Architect
Application Security Architect. CSSLP, OWASP SAMM core team member, ISO 27034 liaison, threat modeling coach, and secure coding coach.
LinkedIn →
Professor & Researcher, AI and Cybersecurity
Professor and researcher working where AI, cybersecurity, and international standards converge. PhD in Cognitive Science Modeling, a Master’s in AI, and 15+ years of experience turning complex technologies into usable, human-centered systems.
LinkedIn →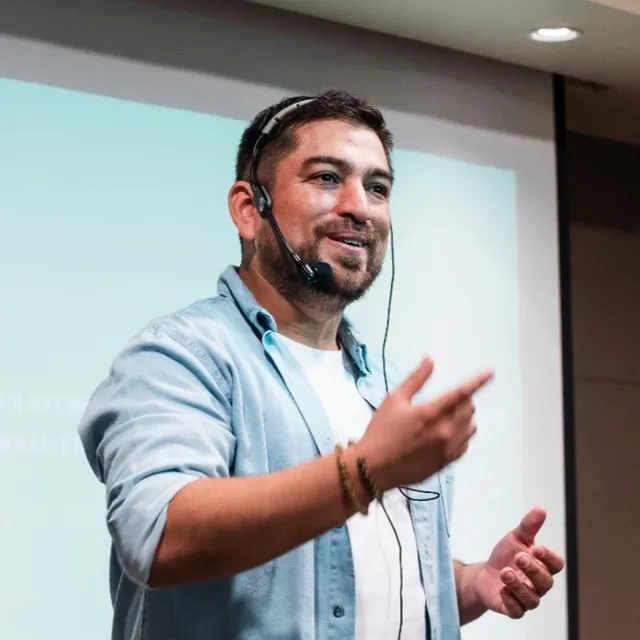
AppSec Program Leader
AppSec Program Leader with 10+ years of experience in banking and finance. CSSLP and CISM certified, active OWASP contributor, and trainer in DevSecOps, S-SDLC, secure design, and threat modeling. He works with teams to secure software from design to delivery.
LinkedIn →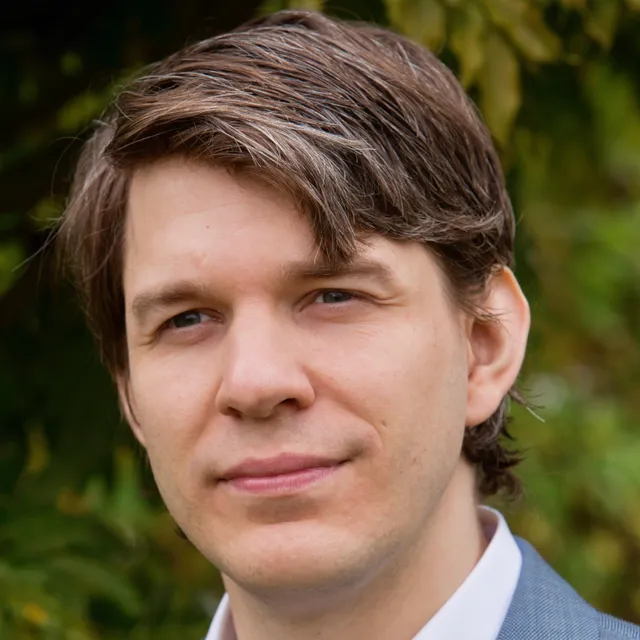
DevSecOps Architect
Timo Pagel is a DevSecOps architect with 25+ years of experience who integrates security into development lifecycles, leads OWASP projects, and provides security training and consulting.
LinkedIn →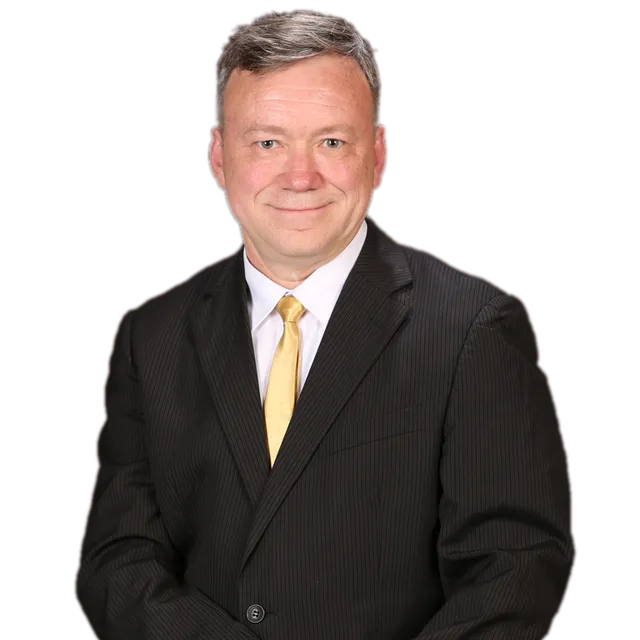
Senior Application Security & Trustworthiness Advisor
Luc Poulin is a veteran application security expert with a doctorate in software engineering and over four decades of experience in IT. He specializes in integrating and auditing security throughout the application lifecycle and contributes internationally to ISO/IEC standards, including as lead editor of ISO/IEC 27034.
LinkedIn →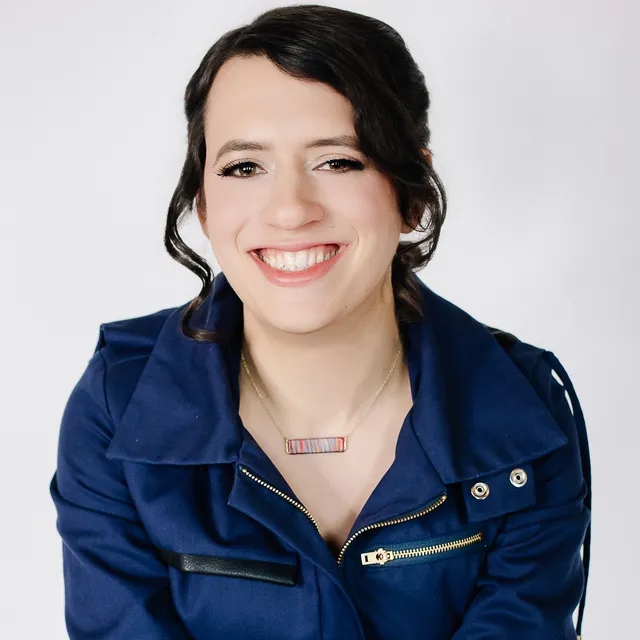
Application Security Architect
Eden Yardeni has built application security programs across several large enterprises. A software engineer by background, she joined the OWASP ASVS working group in 2024 and specializes in security champions programs, threat modeling, and secure software development lifecycles (SSDLCs).
LinkedIn →