Our team
Nariman Aga-Tagiyev
Application Security Architect
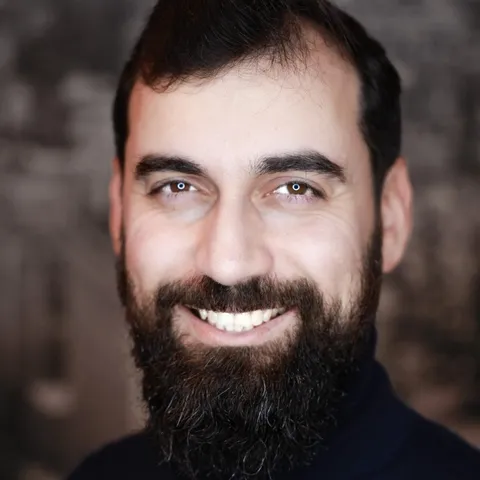
Application Security Architect. CSSLP, OWASP SAMM core team member, ISO 27034 liaison, threat modeling coach, and secure coding coach.
Meet the whole teamArticles by Nariman Aga-Tagiyev
- ENISA's Technical Advisory for Software Bill of Materials: an overview What ENISA's October 2026 SBOM advisory says about fields, formats, the SBOM lifecycle in CI/CD, threats and risks, and what it means for the CRA.
- CPE enrichment for C++ third-party libraries Solving the CPE/PURL gap in Conan-based builds to enable reliable NVD vulnerability matching.
- ENISA's Secure by Design and Default Playbook: an overview What ENISA's July 2026 playbook contains, how its 22 principles and release gates work, and how SMEs can use it for the CRA's secure by design rules.
- ENISA's advisory on the secure use of package managers: an overview The risks of third-party packages and ENISA's four-stage approach to selecting, integrating, monitoring and fixing dependencies, with practical checks.
- The EU Cyber Resilience Act: an executive summary What the CRA is, which products it covers, what manufacturers must prove and by when, and what non-compliance costs. Based on my BSides Krakow 2026 talk.
- CRA harmonised standards: who writes what (October 2026) Where every harmonised standard under request M/606 for the EU CRA stands, by committee and product class, and what it means for your conformity route.
- Deploy OWASP Dependency-Track 5 with PostgreSQL using Docker Compose A production-minded Docker Compose setup for Dependency-Track 5 on your own infrastructure, from first login to SBOM uploads from CI/CD.
- The EU Cyber Resilience Act: a practical guide for SMBs What the CRA means for SMBs as buyers and as makers of digital products, with a vendor checklist, red flags and a five-step compliance roadmap.
- OWASP SAMM Measure and Improve: application security metrics that work Practical guidance for the OWASP SAMM Measure and Improve stream, with example effort, result and environment metrics, and the ones that help with the CRA.
- OWASP SAMM vs. BSIMM: which software security maturity model fits you? How OWASP SAMM and BSIMM differ in purpose, structure, scoring, benchmarks and cost, and how to pick the one that fits you. Based on my RSAC 2025 session.